Cleanup within 12 hours.
Fixed price: $349€199.
For business sites and production portals that can’t stay compromised for long. Priority handling, 24 hours a day, 7 days a week: we remove malware, backdoors and persistence mechanisms from files, the database and the server, and close the door they came in through.
Choose 12 hours
if your site works for your business and every hour counts.
The method is the same for every plan: application and system analysis, full cleanup, hardening and report. Only the guaranteed response time changes.
Your site is a working tool
Company portal, customer area, a site that brings in leads or bookings: as long as it’s infected you lose inquiries, trust and rankings, and waiting for Monday isn’t an option.
Google or your host already flagged the problem
The red Safe Browsing warning, your domain on a blacklist or an ultimatum from your host: you need to act the same day, before the damage spreads.
The infection arrived over the weekend
With the 12-hour plan the clock doesn’t stop at night, on Saturday, Sunday or holidays: we work 24 hours a day, 7 days a week.
You want priority without the emergency cost
Priority handling and half the time of the standard plan, with the same full method: files, database, cron jobs, processes, SQL triggers and entry point.
All the cleanup work.
No hidden fees.
The price is fixed and covers the entire job on a single WordPress installation. What’s left out is written here, before we start.
What’s included
- Analysis of files, core, themes, plugins and uploads, including files obfuscated or encoded with base64, ionCube, Zend Guard and SourceGuardian
- Database analysis: options, content, users, triggers and SQL events
- System checks where access allows: crontab, running processes, users and SSH keys
- Review of Apache, NGINX or LiteSpeed logs, supported by local AI models
- Removal of malware, backdoors and persistence mechanisms, restoring the original files
- Identifying and closing the attack vector, hardening WordPress and the web server
- Technical report and follow-up checks in the hours after the cleanup
- 30-day guarantee: if the malware comes back, we remove it again at no cost
What’s not included
- Multiple WordPress installations, multisite networks or infections spread across an entire hosting account: we prepare a dedicated quote first
- Migration to another server or operating system reinstallation, when needed: these are separate activities, to be agreed upon
- Google and blacklist review times, which depend on external services: we guide you through the request
- Development or fixing of site features unrelated to the infection
If the analysis turns up something outside this scope, we tell you before proceeding and decide together.
From request to report.
In four steps.
No subscription and no software to install: a job with a beginning, an end and an account of what we did.
- 01REQUEST
You contact us
Fill in the form at the bottom of the page or call us. Once the advance payment is complete, we send you instructions for sharing access securely, with no plain-text passwords by email.
- 02ACCESS
The clock starts
The guaranteed 12 hours start from the moment we receive the necessary access. If anything is missing, we tell you right away so no time is lost.
- 03CLEANUP
Analysis and removal
A copy of the current state, application and system analysis, removal of the infection, closing the vector and hardening.
- 04REPORT
Verification and delivery
Clean site back online, technical report and checks in the following hours to confirm nothing regenerates. The 30-day guarantee starts here.
From request to clean site.
Step by step.
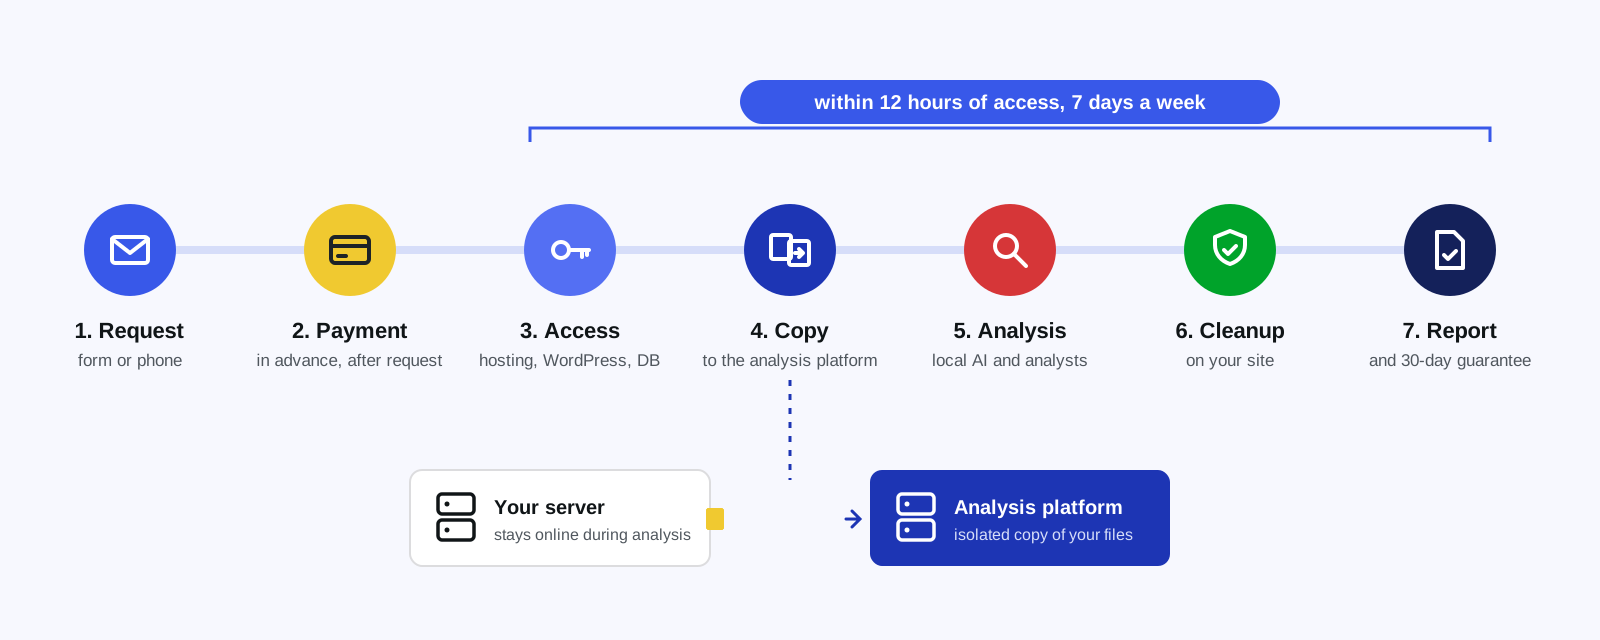
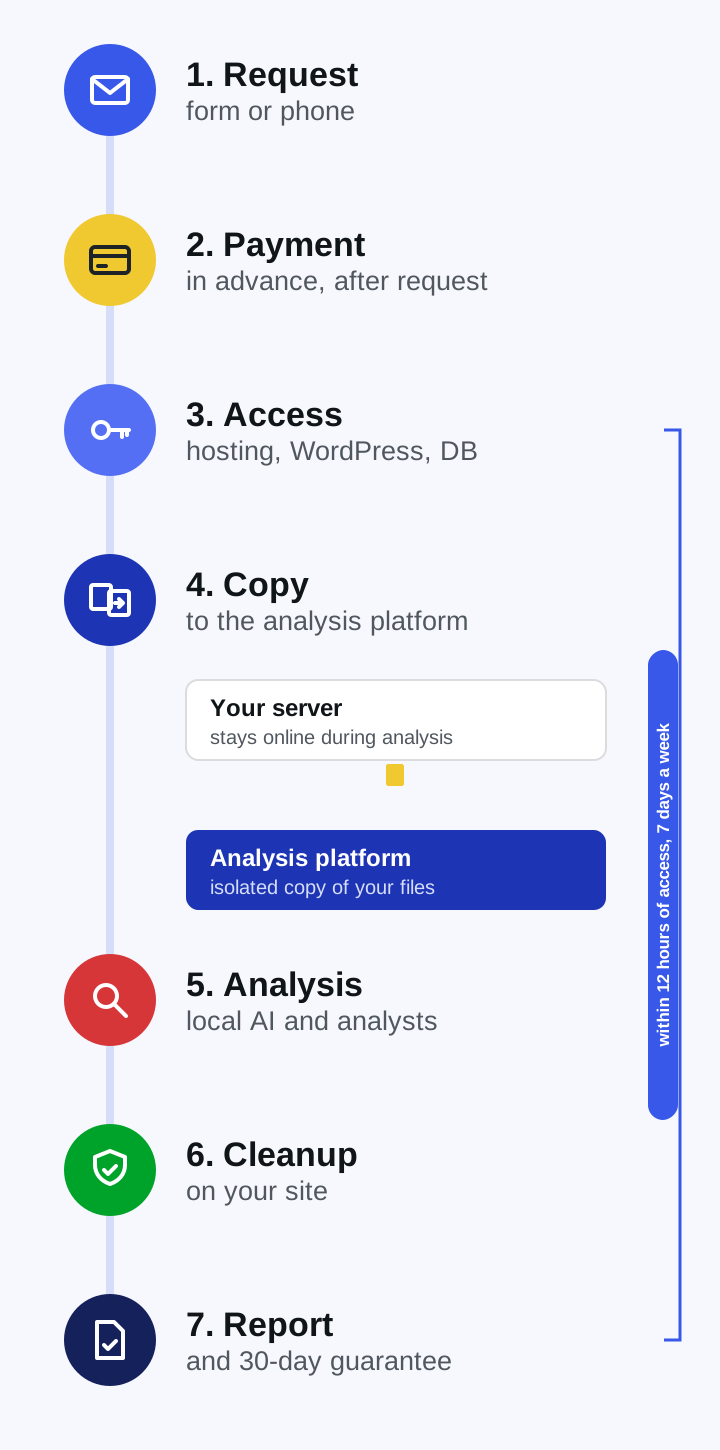
We copy your site’s files to our isolated analysis platform: there we examine them with our tools and local AI models, without straining your server, which stays online meanwhile. The cleanup is then applied to the site.
A few credentials,
shared securely.
On request we sign a non-disclosure agreement. AI analysis runs on our own servers: your site’s data is not sent to third-party services.
- HostingSSH access or, alternatively, control panel and FTP/SFTP. With SSH the analysis also covers cron jobs, processes and system logs.
- WordPressA dedicated administrator user, to be removed when the work is done: we don’t need your personal password.
- DatabaseMySQL credentials or phpMyAdmin access, to look for triggers, hidden payloads and unauthorized users.
- ContextWhat you noticed and since when: warnings, redirects, emails from your host. Every detail shortens the investigation.
- EmailAny emails from users or customers and the anomalies they reported to you.
Within 12 hours of access,
your site is clean and online.
- The clock starts when we receive the necessary access, not at first contact, so the time depends only on our work. It applies 7 days a week, holidays included.
- If we exceed the guaranteed time we refund the difference; if the cleanup isn’t completed by the maximum deadline, the contract is terminated and we refund the full amount, as explained in the FAQ.
- If the analysis reveals other compromised sites or a system-level infection, we tell you before proceeding.
- After the cleanup we check that the infection doesn’t regenerate and document everything in the report.
- 30-day guarantee: if the malware comes back within 30 days of the cleanup, we remove it again at no charge.
Before you choose.
Answers to the questions we get asked most often about the 12-hour plan.
What happens if the infection comes back?
You have a 30-day guarantee: if the malware comes back within 30 days of the cleanup, we remove it again at no charge. In the hours after the job we also check that no suspicious files, users or processes reappear, and if the infection returns we look for the reason why: if it stems from a new vulnerability, for example an outdated plugin, we point it out along with the fixes to make.
How do I pay?
Payment is in advance: it happens right after the request, before work begins. You can pay by credit or debit card through Stripe, or by bank transfer, including instant transfer. As soon as we receive payment we send you instructions for sharing access, and that’s when the 12 hours start. If you’re in a hurry choose card or instant transfer: a standard bank transfer can take one or more business days to clear.
Will I get an invoice?
Yes. For every job Managed Server S.r.l. issues a regular electronic invoice and sends you a courtesy copy by email. You enter your billing details in the order form: company name and VAT number with recipient code or certified email (PEC) if you’re a business, tax code if you’re an individual. For businesses in other EU countries with a valid VAT number on VIES, the invoice is issued without VAT, under the reverse charge.
Do the 12 hours also apply on weekends?
Yes: with the 12-hour plan we work 24 hours a day, 7 days a week, Saturdays, Sundays and holidays included. The clock starts when we receive your access, whatever time it arrives.
What happens if you miss the 12 hours?
If we exceed 12 hours but finish within 24, we refund the difference from the 24-hour plan, i.e. €100 + VAT. If we don’t finish within 24 hours, the contract is automatically terminated and we refund the full amount within 24 business hours, without you having to ask. Continuing the job requires a new agreement.
Can I switch to the 6-hour plan?
Yes. If at first contact it turns out your site can’t wait even 12 hours, for example an e-commerce store that is losing orders, we suggest the 6-hour plan before starting. The method stays identical; only the guaranteed time changes.
Do you work on any hosting?
Yes: shared hosting, VPS, dedicated servers and cloud, with Apache, NGINX or LiteSpeed. With SSH access we extend the analysis to cron jobs, processes and system logs; with only FTP and the control panel we work on files and database and tell you which checks remain excluded.
Is my site’s data safe?
We work with dedicated credentials that we ask you to revoke when the job is done, and on request we sign a non-disclosure agreement. The AI models we use run on our own servers: files and logs are not sent to third-party services.
Does the site stay online during the cleanup?
Normally yes. If the site is distributing malware to visitors or stealing data, it may need to go into maintenance mode for the strictly necessary time: we suggest it and decide together.
What does the report contain?
The infection components we found and where they were, how we removed them, the vector used to get in and the hardening measures applied, with the fixes we recommend you make afterward.
Cleanup within 12 hours.
Let’s start here.
Tell us the site and what you noticed, enter your billing details and pay in advance by card or bank transfer. As soon as we receive payment we send you instructions for sharing access: from that moment the 12 hours start.
$349 + VATPrevious price: €299 €199 + VAT · fixed price per single WordPress installation
Electronic invoice from Managed Server S.r.l. · 30-day guarantee · terms of sale
Prefer the phone? +39 02 5656 9681 · Monday–Friday,
$349€199 + VAT · 12 hours
Order